Course: ITN 276 – Computer Forensics
Artifact Type: Digital Forensics Investigation Lab
Semester: Spring 2024
Overview
This lab involved conduction a digital forensic investigation of a suspicious login attempt. Using Paraben E3, I examined digital evidence associated with the incident to identify information that could help retrace the activity that occurred. The investigation required me to look into multiple sources of evidence, document relevant findings, and prepare information that could be used in an incident response investigation
My Work
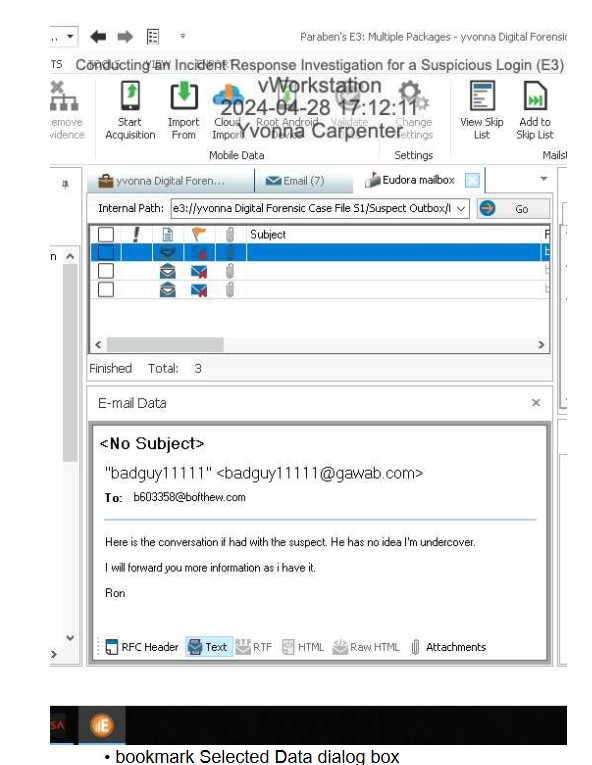
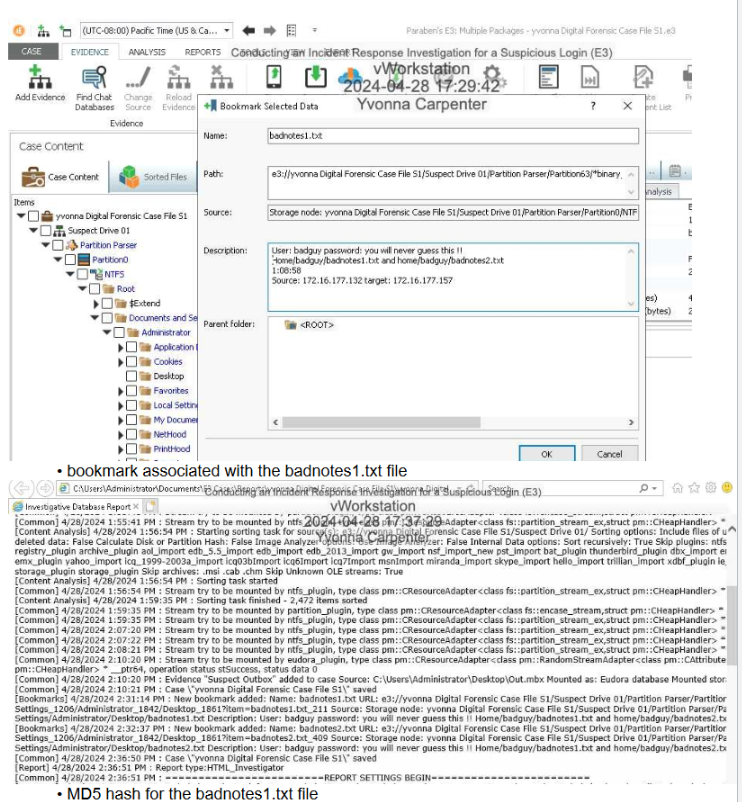
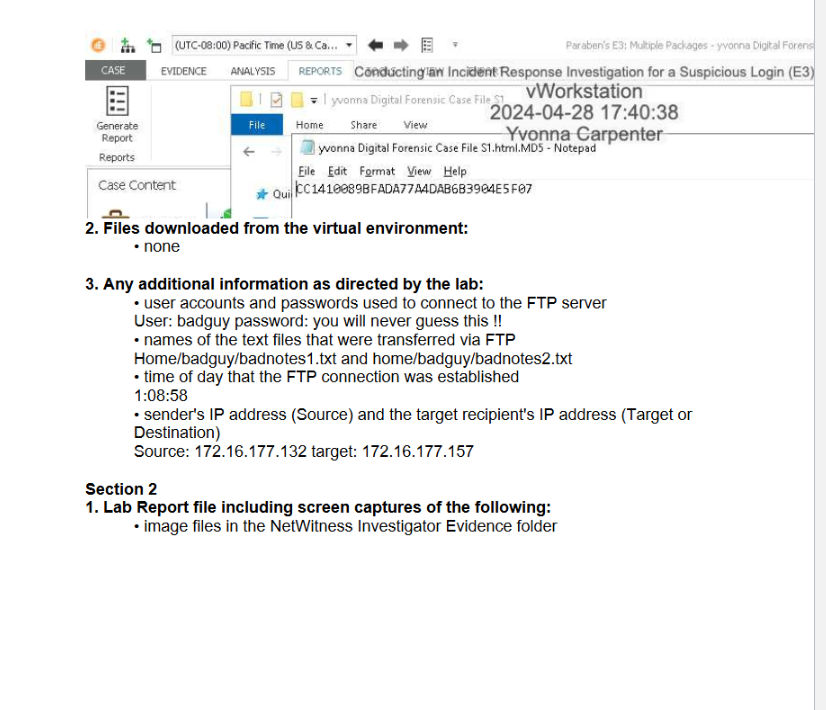
During the investigation, I identified evidence of suspicious activity. This included reviewing activity with an FTP connection, identifying files transferred through the connection, documenting the connection time, and identifying the source and destination IP addresses. I also found incriminating email evidence and bookmarked relevant information within the software. As I worked through it, I gathered my findings through screenshots to support the investigation. I also generated forensic reporting information and recorded evidence such as the MD5 hash associated with an identified file.
Artifact
Skills Demonstrated
This lab strengthened my cybersecurity analysis and investigation skills by requiring me to examine multiples pieces of digital evidence and determine which information was relevant to an incident. Rather than looking at each piece separately, I had to connect details such as file activity, network information, timestamps, and email evidence to better understand the activity being investigated.
The lab also have me hands-on experience documenting forensic findings in a structured manner. It reinforced the importance of carefully examining evidence and approaching digital investigations in a thorough and systematic way.