Course: CYSE 301 – Cyber Techniques & Operations
Artifact Type: Network Traffics Analysis Lab
Semester: Spring 2025
Overview
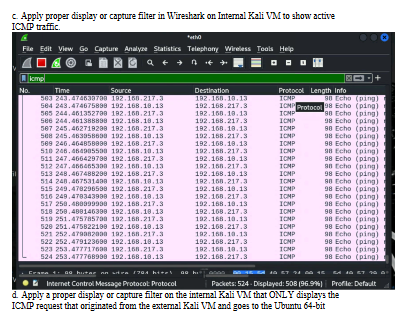
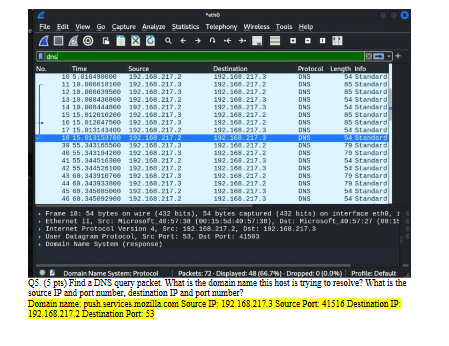
This lab focused on capturing and analyzing network traffic using Wireshark in a virtual lab environment. I examined different types of network communication, including ICMP, DNS, and FTP traffic. The lab required me to apply Wireshark filters, look at individual packets, identify important network information, and use captured traffic to understand how data was being communicated between systems.
My Work
During the lab, I analyzed ICMP traffic to identify information such as source and destination IP addresses, sequence numbers, data size, and response time. I also looked into DNS queries and responses to identify the systems involved, port numbers, and the results returned by the DNS server. Another portion of the lab involved looking into FTP traffic in a controlled virtual environment. By analyzing the captured packets, I was able to observe information being transmitted during an FTP connection and see how network traffics can expose information when a protocol does not protect the data being transmitted. Which helped me connect packet analysis with the security risks associated with network communication.
Artifact
Skills Demonstrated
Using Wireshark taught me to move from a large packet capture to specific information that could help explain network activity. Filters allowed me to isolate ICMP, DNS, and FTP communications and examine the details contained within individual packets. The lab also demonstrated why packet analysis is valuable in cybersecurity. Being able to recognize what systems are communicating, what protocols are being used, and what information may be visible on the network can provide important context when investigating network behavior.